How to Read PE Headers in a DLL File
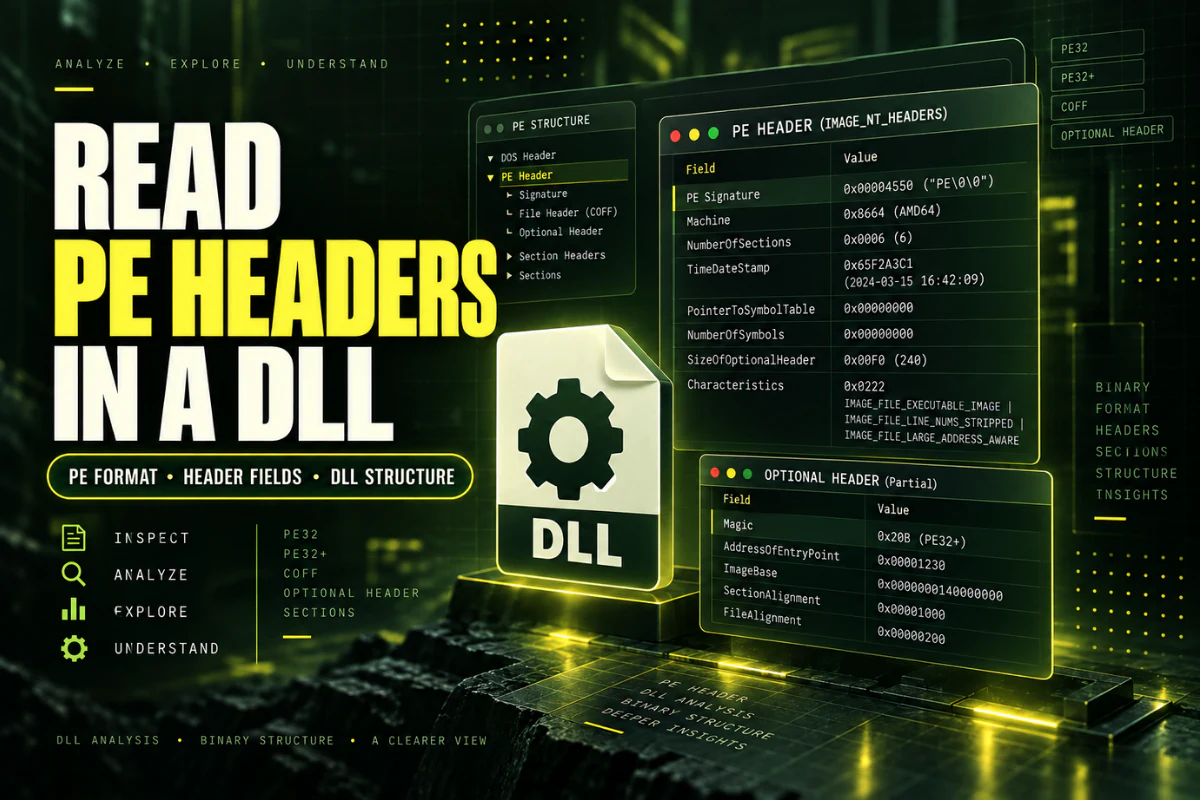
A DLL file contains several headers that tell Windows what kind of binary it is, which architecture it targets, where its sections are located, and how the operating system should map it into memory.
These headers are part of the Portable Executable format, usually shortened to PE.
You do not need to read raw hexadecimal bytes to understand the most useful fields. A DLL PE header viewer can decode the structure and show the values in a readable format.
This guide explains how PE headers are organized, which fields matter most, and how to use them when inspecting a DLL.
Use our DLL PE header viewer to inspect architecture, PE32 or PE32+, entry point, image base, sections, imports, exports, and hashes without running the DLL.
On this page
What Is a PE Header?
A PE header is a group of structures near the beginning of a Windows executable file.
PE stands for Portable Executable. The format is used by several Windows file types, including:
- EXE files
- DLL files
- SYS driver files
- Some other Windows executable images
The PE header gives Windows the information it needs to understand the binary before loading it.
For a DLL, this includes the target architecture, the number of sections, important memory values, data-directory locations, and image characteristics.
PE Header Layout at a Glance
The structure can look complicated at first, but the main parts are easy to separate.
↓
DOS Stub
↓
PE Signature
↓
COFF File Header
↓
Optional Header
↓
Data Directories
↓
Section Table
Each part has a specific purpose.
1. DOS Header
The DLL begins with a DOS header.
The first two bytes normally contain the letters:
This is often called the MZ signature.
The DOS header also contains an important field called e_lfanew. This value points to the location of the PE header later in the file.
For most users, the key facts are simple:
- The file often starts with
MZ. e_lfanewpoints to the PE signature.- A missing or invalid structure may indicate the file is not a normal PE image.
2. PE Signature
At the offset stored in e_lfanew, a valid PE file normally contains this signature:
The two zero bytes are part of the signature.
This value confirms that the file contains a PE structure at that location.
A PE viewer checks this automatically. You normally do not need to calculate the offset yourself.
3. COFF File Header
After the PE signature comes the COFF File Header.
This header contains several useful fields.
| Field | What it tells you |
|---|---|
| Machine | The target processor architecture |
| NumberOfSections | How many PE sections are listed |
| TimeDateStamp | A build-related timestamp field |
| SizeOfOptionalHeader | Size of the Optional Header |
| Characteristics | Flags describing the image |
The Machine Field Shows Architecture
The Machine field is one of the most useful PE values.
Common values include:
0x8664 = x64
0x01C0 = ARM
0xAA64 = ARM64
A viewer translates these values into readable architecture names.
If you only need to know whether the DLL is 32-bit or 64-bit, this field is more reliable than guessing from the filename or folder.
See How to Check Whether a DLL Is 32-Bit or 64-Bit for a full guide.
4. Optional Header
The name Optional Header is slightly misleading.
For normal PE executable images, this header contains important loading information and is not something you would normally ignore.
It includes fields such as:
- Magic value
- AddressOfEntryPoint
- ImageBase
- SectionAlignment
- FileAlignment
- SizeOfImage
- Subsystem
- DLL characteristics
- Number of data directories
5. Magic Value: PE32 or PE32+
One of the first fields in the Optional Header is commonly called Magic.
Typical values are:
The plus sign does not mean the file is simply a newer version. It refers to the 64-bit form of the PE Optional Header.
6. Address of Entry Point
AddressOfEntryPoint is a relative virtual address that points to the entry location used when the image starts.
For a DLL, this is related to initialization when Windows loads the image.
You may see a value such as:
For basic file identification, you usually do not need to interpret the address deeply.
It becomes more useful during debugging, reverse engineering, or binary comparison.
7. Image Base
The ImageBase field contains the preferred virtual address where the image would like to be mapped.
Example:
Windows may load the DLL at a different address when necessary.
Modern systems use address randomization and relocation mechanisms, so the preferred image base is not always the final runtime address.
8. Section Alignment and File Alignment
PE files have one layout on disk and another layout when mapped into memory.
FileAlignment controls how section data is aligned in the file.
SectionAlignment controls how sections are aligned in memory.
Typical values might look like:
SectionAlignment: 0x1000
Most users do not need to change or calculate these values. They are mainly useful for understanding the file layout.
9. Subsystem
The Subsystem field tells Windows what kind of environment the image expects.
Common values can indicate:
- Windows GUI
- Windows console
- Native system environment
- EFI applications in other PE contexts
For DLL inspection, this field is usually secondary to architecture, imports, exports, and sections.
10. DLL Characteristics
The Optional Header also contains flags called DLL characteristics.
These can describe security and loading features supported by the image.
Depending on the binary and viewer, you may see flags related to:
- Address space layout randomization support
- Data execution prevention compatibility
- High-entropy virtual address support
- Other image loading behavior
These flags are technical properties. They are not a simple good-or-bad security score.
11. Data Directories
Data directories point to important tables and structures inside the PE file.
Examples include:
| Directory | What it points to |
|---|---|
| Export Directory | Exported functions and symbols |
| Import Directory | Imported libraries and functions |
| Resource Directory | Icons, strings, version data, and other resources |
| Base Relocation Directory | Relocation information |
| CLR Runtime Header | Managed .NET metadata information |
These directories are how a PE parser finds many of the features shown in a DLL analyzer.
12. Section Table
After the main headers comes the section table.
Each section header describes a region in the file.
A section entry can include:
- Section name
- Virtual size
- Virtual address
- Raw data size
- Raw file offset
- Section characteristics
Common sections include .text, .data, .rdata, .rsrc, and .reloc.
Which PE Header Fields Matter Most for Normal Users?
If you are not doing reverse engineering, focus on a small set of fields.
Can PE Headers Tell You If a DLL Is Safe?
No.
PE headers can tell you how a file is structured, but they cannot prove that the code is harmless.
A malicious DLL can still have valid PE headers, common section names, and normal imports.
Use PE headers for file identification and technical analysis. Do not treat them as a malware verdict.
How PE Headers Connect to Imports and Exports
The PE headers include data-directory entries that point to the import and export structures.
This is why one DLL analyzer can show both header fields and higher-level information such as imported libraries and exported functions.
For more detail, read How to View DLL Imports and Dependencies and How to View DLL Exports Online.
A Simple PE Header Reading Order
If you are learning the format, read the file in a fixed order. Confirm the MZ signature, follow e_lfanew to the PE signature, read the machine type, check PE32 or PE32+, then move to data directories and sections. This keeps the structure easier to understand and prevents you from getting lost in less important fields too early.
Frequently Asked Questions
What is a DLL PE header?
It is a set of Portable Executable structures that describe the DLL’s architecture, layout, loading information, sections, and data directories.
What does MZ mean in a DLL?
MZ is the traditional DOS header signature found at the beginning of many PE files.
What does PE32 mean?
PE32 is the common 32-bit form of the PE Optional Header.
What does PE32+ mean?
PE32+ is the 64-bit form of the PE Optional Header.
Which PE field tells me x86 or x64?
The COFF Machine field is the main architecture identifier.
Can I read PE headers without running the DLL?
Yes. PE headers can be parsed directly from the file as binary data.
The Best Way to Read DLL PE Headers
Start with the architecture and PE format.
Then look at the number of sections, entry point, image base, data directories, imports, and exports as needed.
You do not need to memorize every hexadecimal value. A PE header viewer can translate the structure into readable fields and help you focus on what matters.
For a broader overview, see DLL Analyzer Online: What Information Can You Find?.
Read your DLL PE headers online
Inspect architecture, PE32 or PE32+, entry point, image base, sections, imports, exports, and hashes.
View DLL PE Headers